Advisory Detail
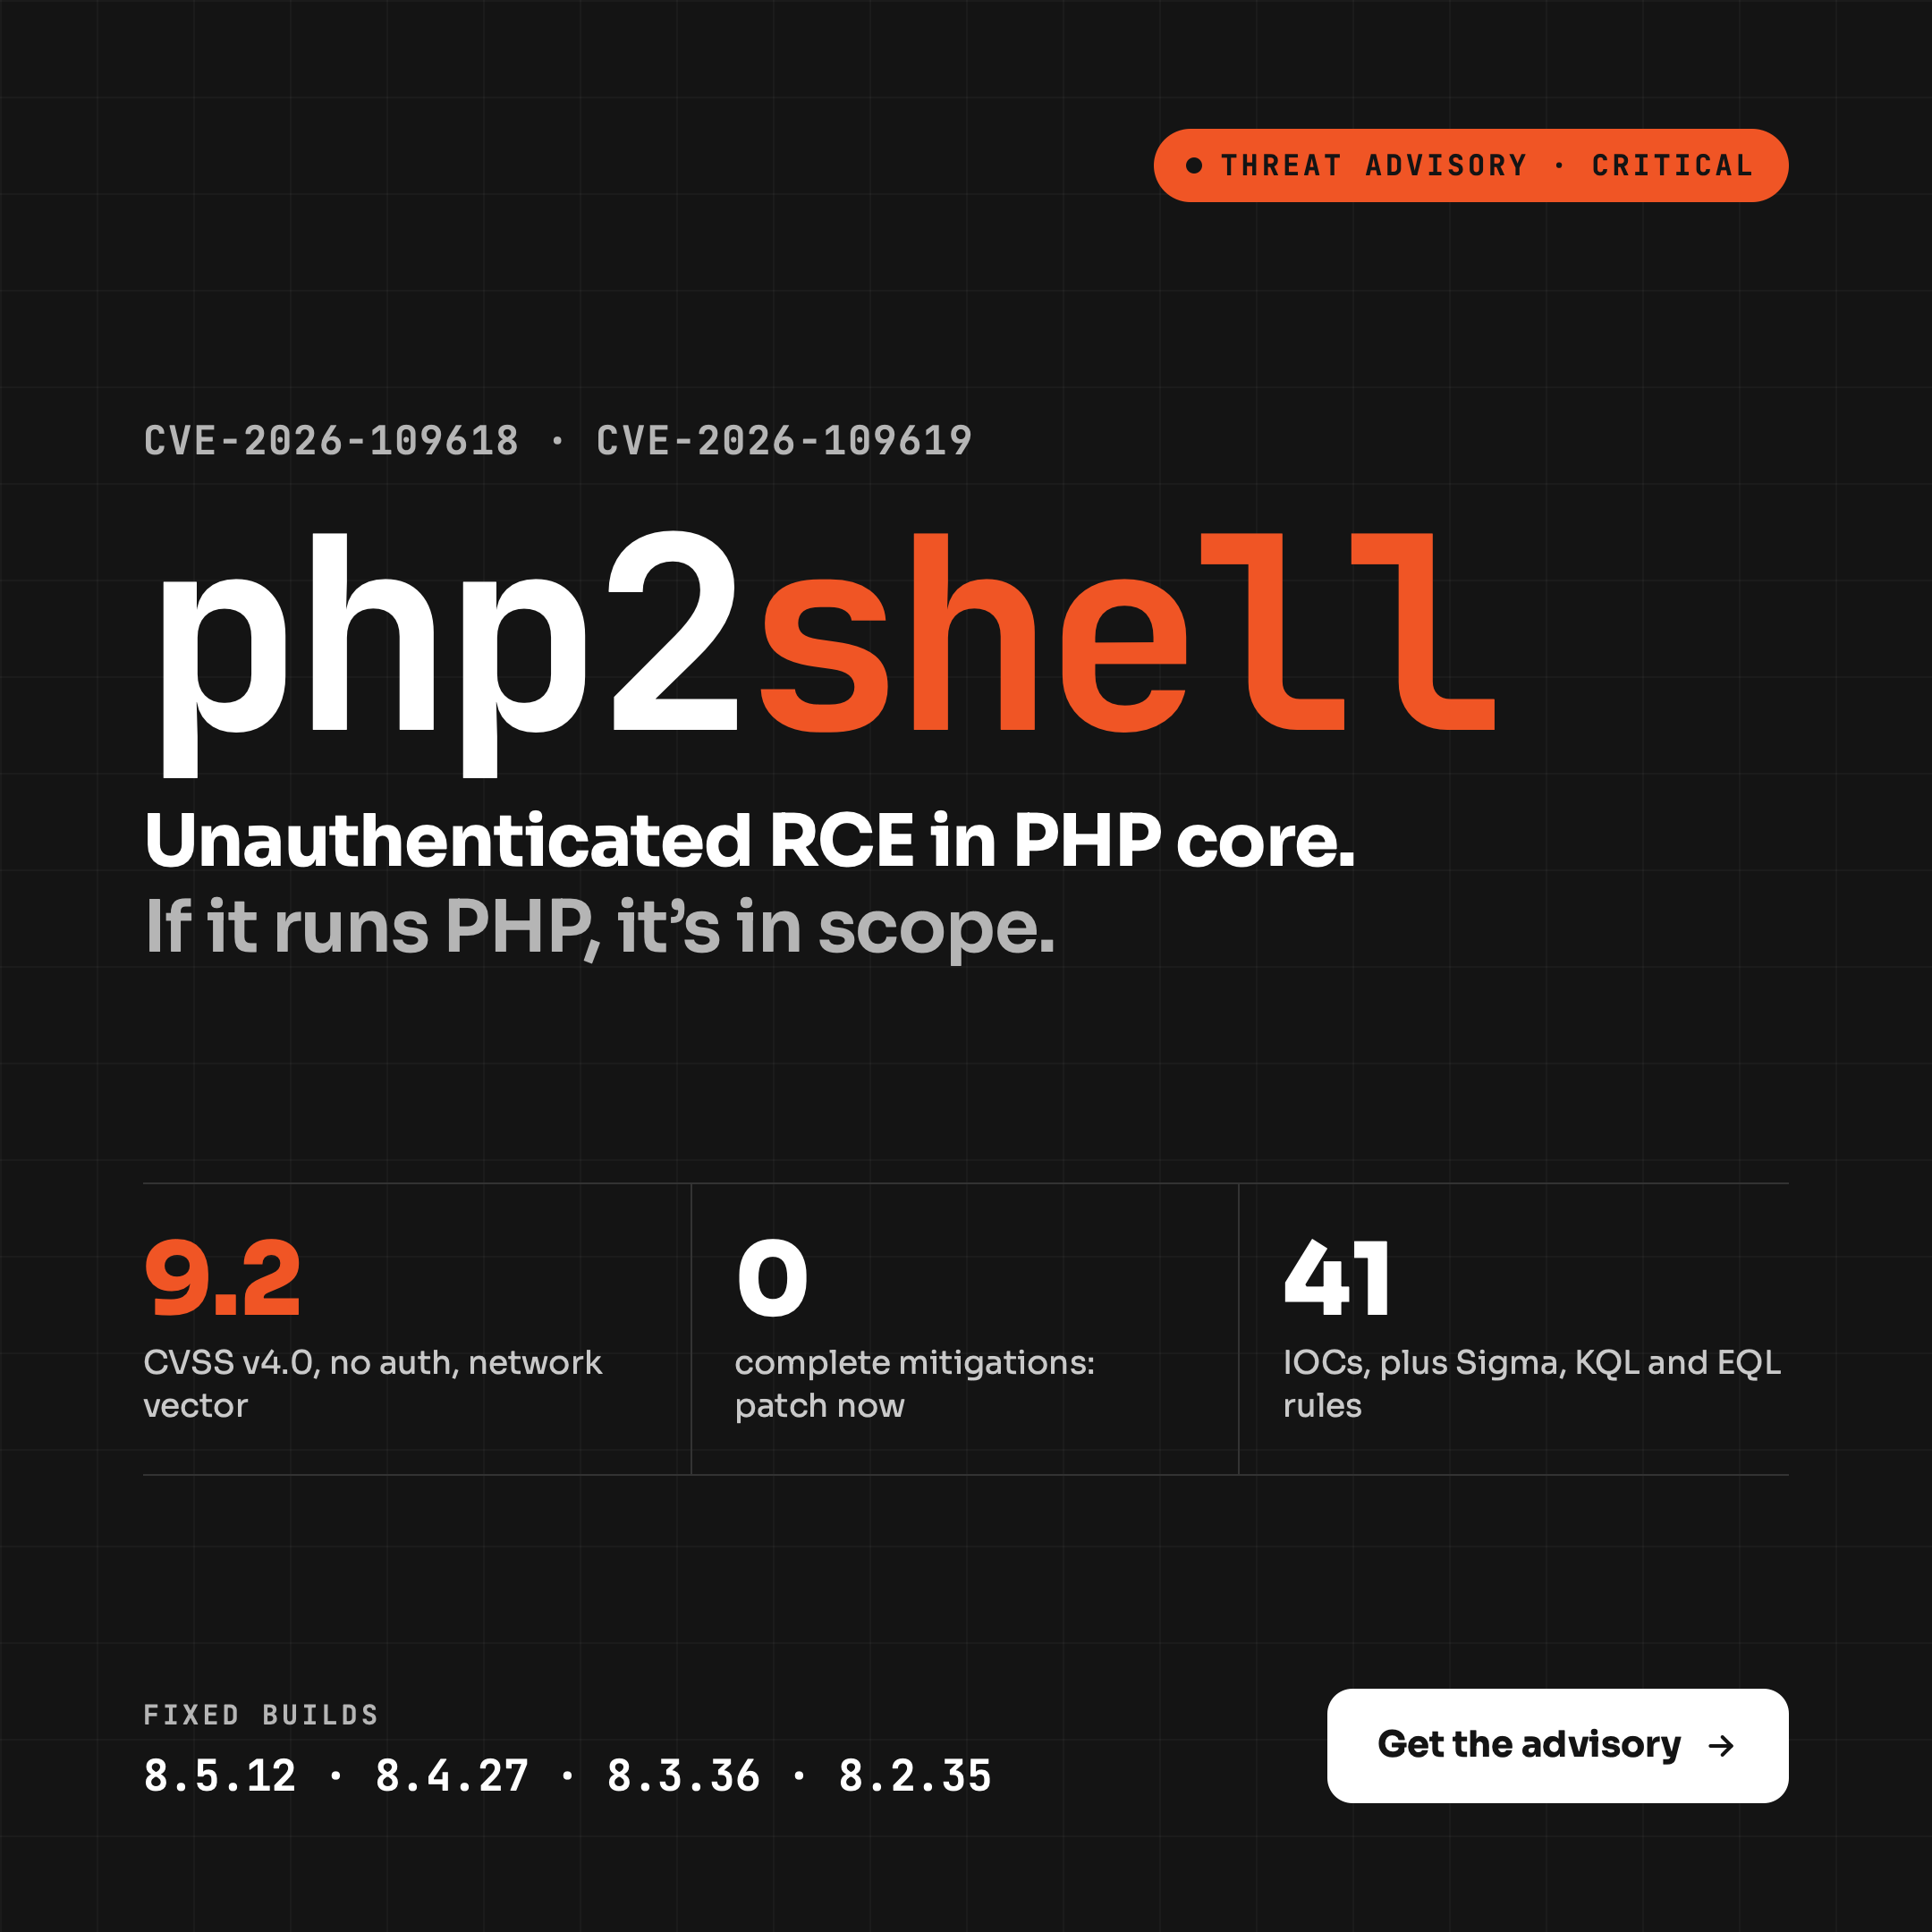
The recently uncovered "php2shell" vulnerabilities (CVE-2026-109618 and CVE-2026-109619) pose a critical threat to global web infrastructure, carrying a 9.2 CVSS score and affecting all PHP core versions after 5.4. Attackers leverage crafted POST requests to trigger out-of-memory errors during request startup, allowing them to either achieve unauthenticated remote code execution for full server takeover or silently siphon sensitive process memory like API keys and passwords.
Immediate patching to fixed builds (8.5.12, 8.4.27, 8.3.36, or 8.2.35) is the only safe choice, because the PHP security team explicitly states there are no complete mitigations.
To help security operations centers (SOCs) manage this urgent threat, AiStrike delivers an end-to-end detection and response framework.
The AiStrike platform automatically correlates weak signals into a single, AI-triaged case enriched with critical exposure context. It also equips security teams with ready-to-deploy detection rules, retroactive threat hunting, and automated playbooks to instantly isolate compromised hosts and rotate exposed secrets.
Download the full white paper for our comprehensive technical breakdown, ready-to-deploy Sigma rules, and complete list of IOCs.
PHP2Shell Advisory Report