Advisory Detail
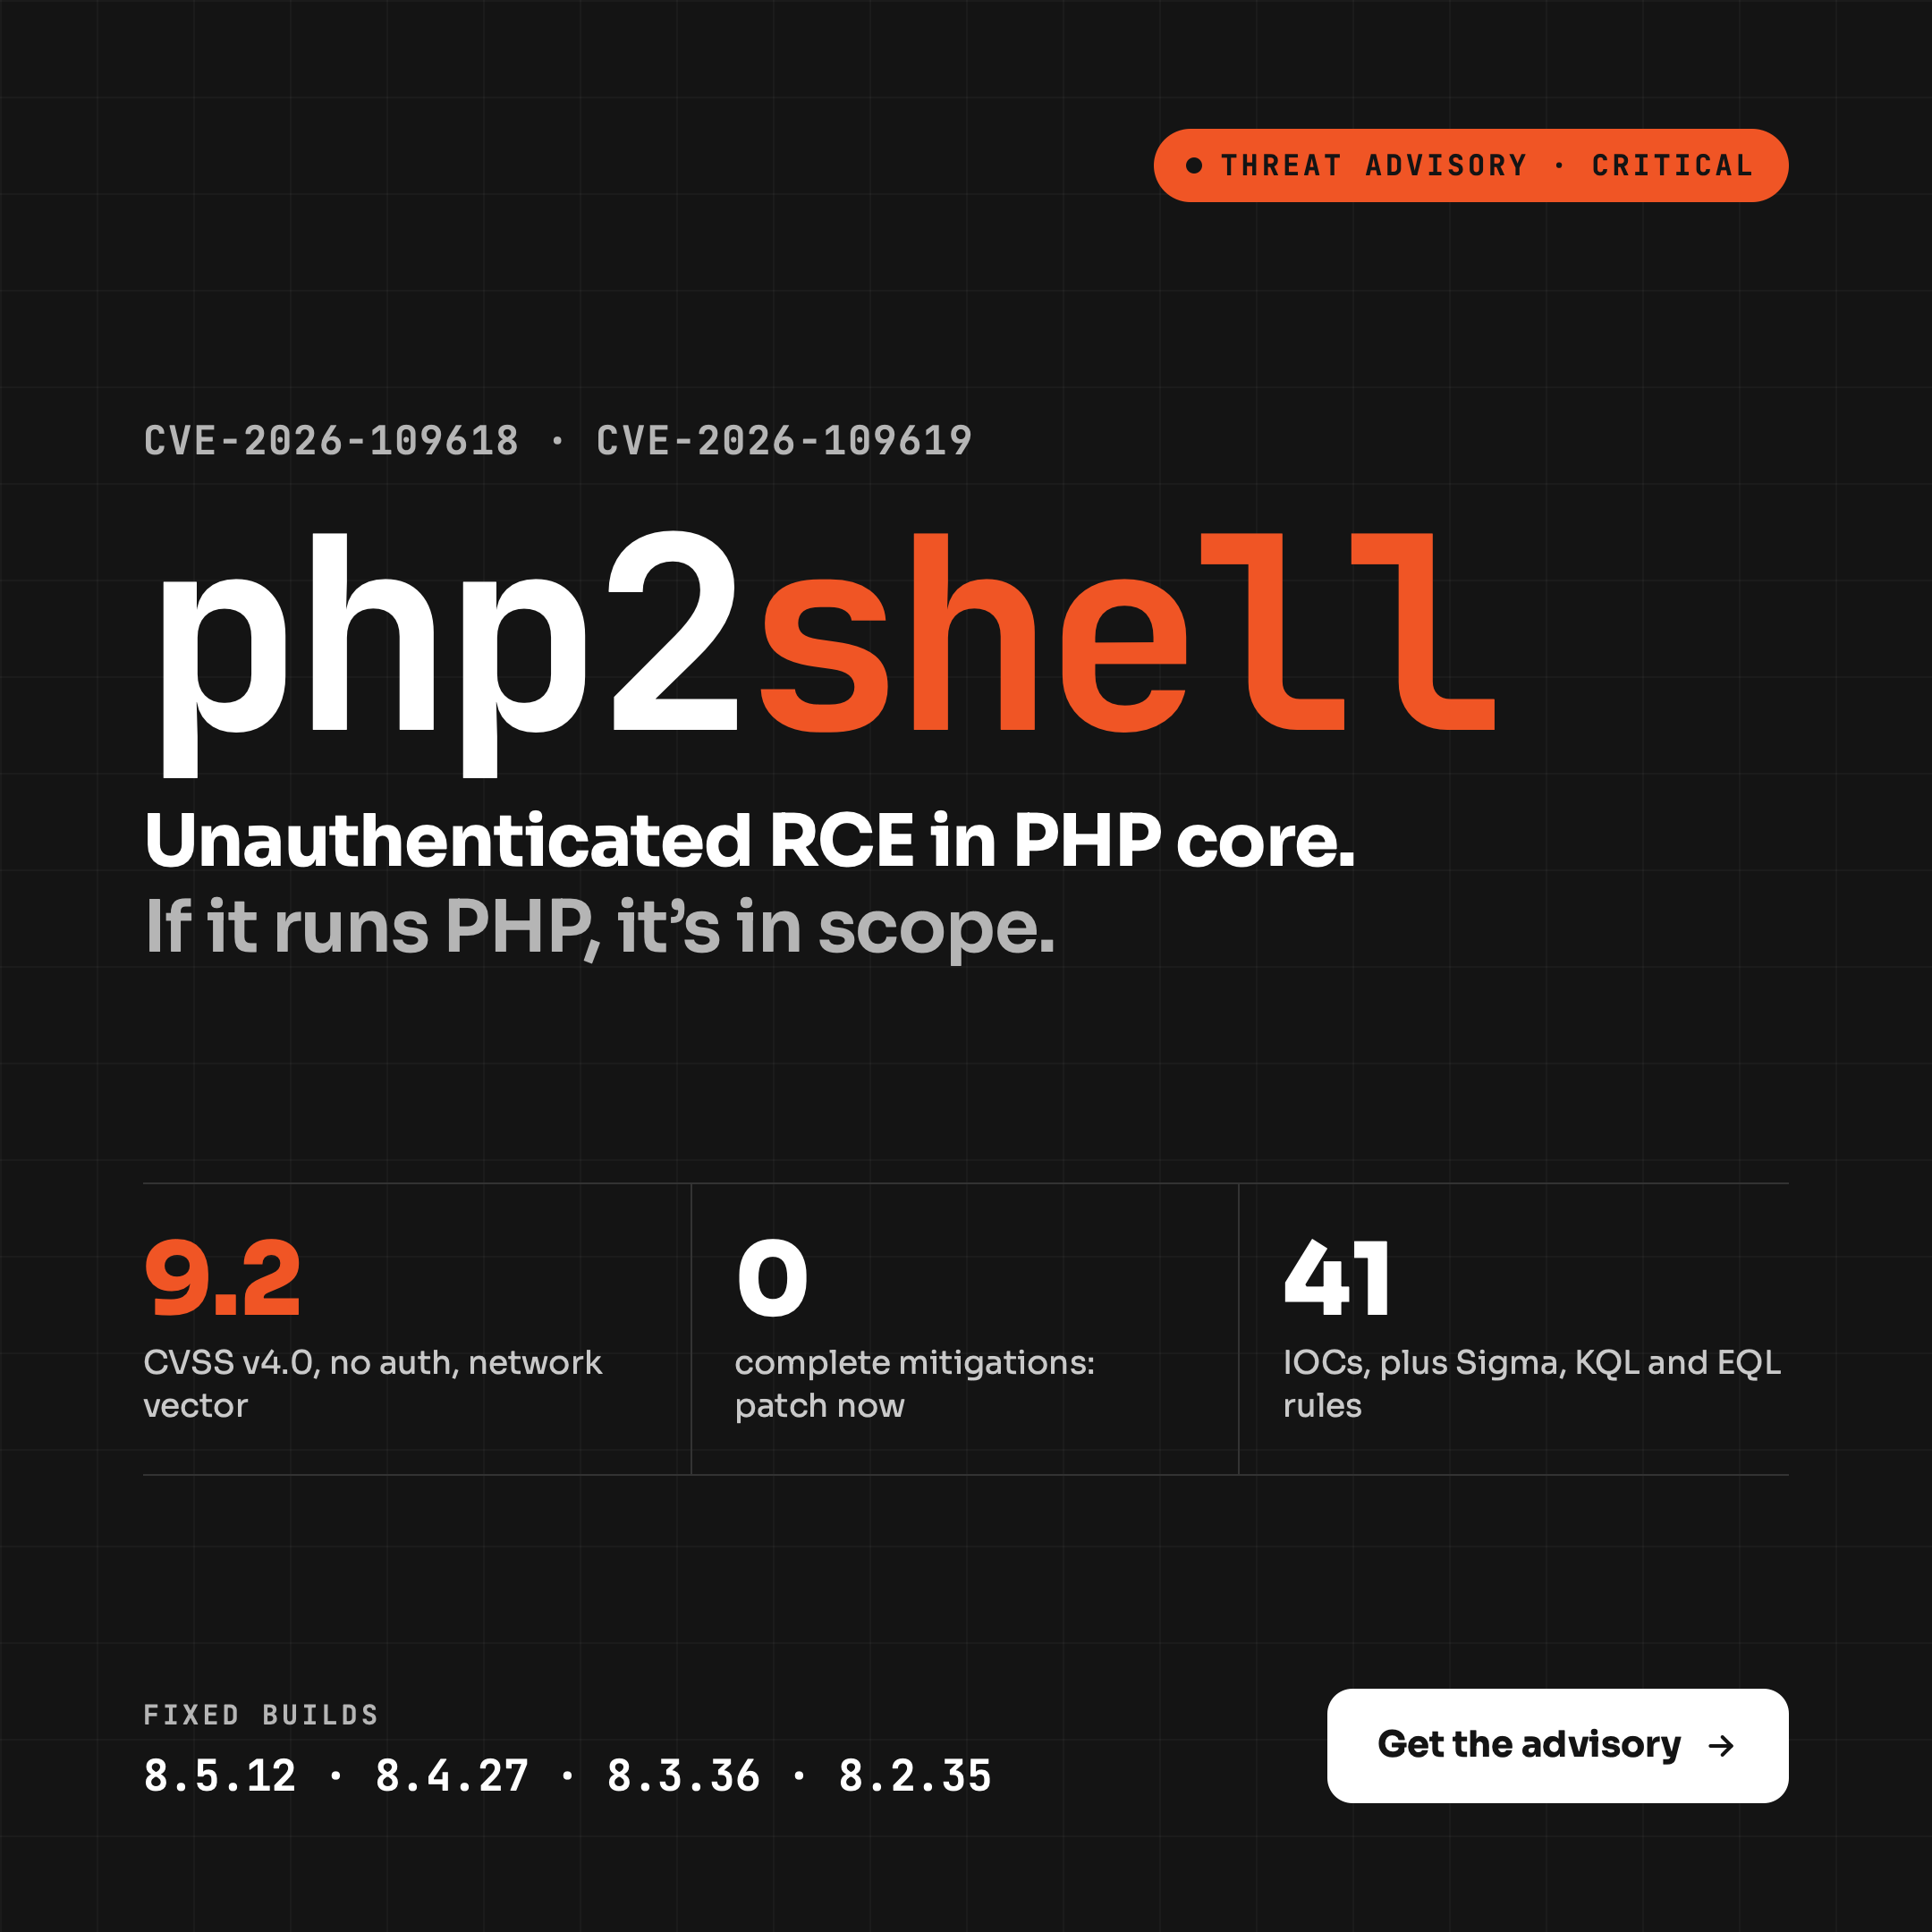
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a critical pre-authentication remote code execution flaw in PHP request handling, scored 9.2 on CVSS v4.0. From 21 October to 1 November 2026, GreyNoise recorded 245,083 attack sessions, including 213,331 exploitation attempts. Scanning started on 21 October, the day PHP shipped the fix. The first confirmed remote code execution followed on 28 October, and by 29–31 October operators were opening reverse shells, planting SSH access, running Gitleaks and LinPEAS, querying cloud metadata, and uploading stolen data. Those attempts produced 1,177 confirmed shells. Five source IPs were behind every one of them, while 509 related attacker IPs across 56 countries kept the scanning noisy. 262 of those IPs are block candidates.
The exploit runs inside PHP before any application code, so login pages, in-app validation, and route authorisation never see it. Patch to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restart PHP workers. Hundreds of scanners feed a single post-exploitation controller, so IP blocking goes stale quickly. Hunt back to 21 October for reverse shells, new SSH keys under web-server accounts, cloud metadata queries, and outbound archive uploads.
Download the full white paper for our comprehensive technical breakdown, ready-to-deploy Sigma rules, and complete list of IOCs.
Advisory Report